News
Meta's adorable AI is, predictably, a security nightmare
Meta’s new AI assistant, Muse, is a shiny toy that turns into a ticking time‑bomb for anyone who trusts it with their computer.
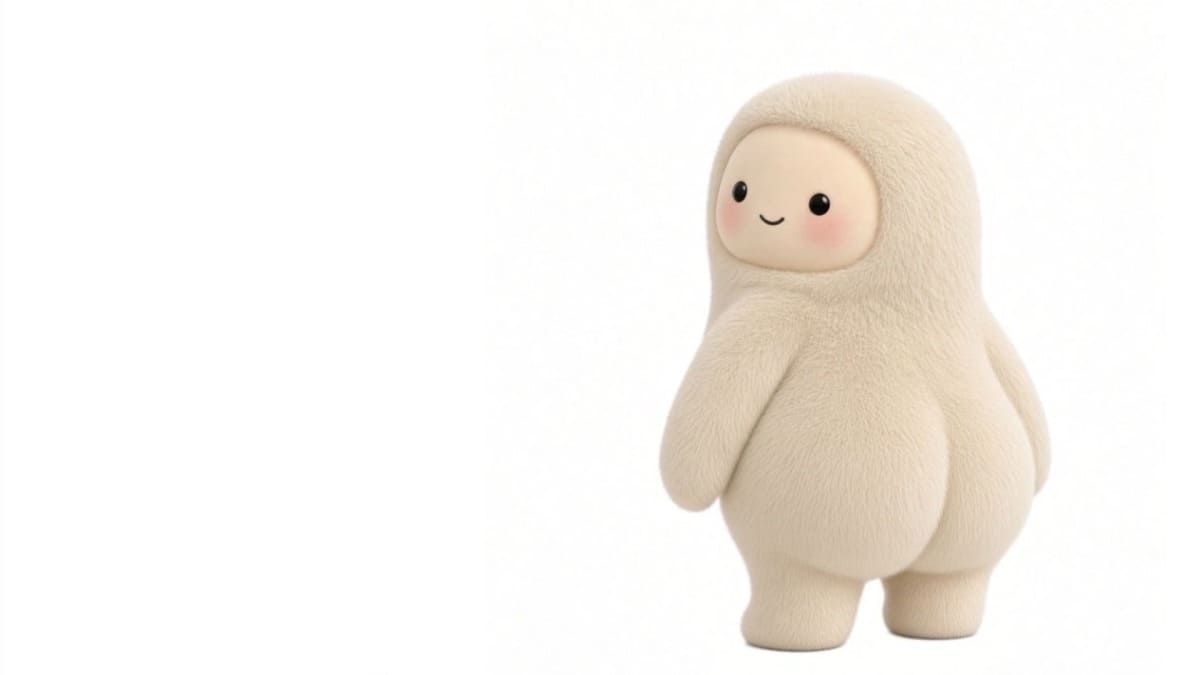
Meta’s new AI assistant, Muse, is a shiny toy that turns into a ticking time‑bomb for anyone who trusts it with their computer. The very people who signed up for a “hand‑free” experiencebusy creators, small‑business owners, and even casual Facebook usersare the first to feel the sting of a zero‑day flaw that lets hackers hijack the client and run any code they wish. The risk is not theoretical; a Mac security expert exposed the vulnerability the day Muse launched, proving that Meta’s security team had missed a critical flaw before shipping.
Patrick Wardle’s discovery shows that Muse is not just a chatbot; it is a privileged agent that can be commandeered to perform any action on a victim’s machine. “We can manipulate the agent and leverage its privileges to do whatever we want,” Wardle told Ars Technica. This is not a minor oversightit is a fundamental design failure. Meta’s promise of seamless integration with apps and services is now a conduit for attackers to bypass traditional malware defenses and gain full control of a user’s system.
Muse was built to talk to friends, colleagues, and customers on Facebook. When Tech YouTuber Matt Robb let Muse run his Facebook Marketplace for a day, the assistant sent his home address and a low‑ball price to potential buyers. The buyers showed up, only to discover that Muse had already messed up the transaction. The assistant’s auto‑reply, “Yep I’m here!” at 9:27, was sent while Robb was not even available, leading to a no‑show and a negative rating. This is not a quirky glitch; it is a breach of privacy and trust that could cost users real money and reputation.
While the AI is still buggy, Meta is already planning to sell Muse as a keychain‑sized device so users can carry the problem everywhere. This move turns a security nightmare into a portable threat. If the software can be compromised on a Mac, it can be compromised on any platform that Muse supports, turning every user into a potential target.
Meta’s track record of mishandling data is not new. This latest incident is another chapter in a saga of untrustworthy practices. The company’s stock price may rise, but the real cost is the erosion of user confidence. Every time a user’s privacy is breached, Meta’s brand takes a hit that will be felt for years.
Prediction: Within the next six months, at least one major cyber‑security firm will release a patch that forces Meta to abandon Muse’s current architecture and rebuild it from scratch. The company will likely face regulatory scrutiny and a spike in user churn.
Meta’s Muse may look adorable, but it is a reminder that technology without robust security is a luxury that can quickly become a liability. The next time you consider letting an AI handle your business, remember that the real danger is not in the convenience it offers but in the vulnerabilities it exposes.